Cybersecurity consulting firm
Secure today,
Protect tomorrow.
Kumaiko supports executives, investors and their teams (security, IT, legal, compliance) in managing their cyber risks, in France and internationally. We translate cybersecurity into business decisions: clear for an executive committee, robust for an expert.
- Governance · Risk · Compliance · Resilience
- Fractional CISO
- France & international
The real problem
Cybersecurity is not just a technical issue.
In many organizations, cybersecurity is still seen as an engineering topic: tools, code, penetration tests. Until an incident occurs and reveals that the company’s essential assets were not protected.
-
Critical activities not identified
Systems get protected, but not the processes that keep the business running.
-
No governance
No clear owner, no formalized processes, total dependence on a few individuals.
-
Untested resilience
When an incident hits, no one really knows what to restart first, or who decides.
-
Reactive compliance
NIS2, DORA, ISO 27001, SOC 2: requirements from regulators and customers keep piling up, and now put executives’ liability on the line. Teams don’t know where to start.
-
Exposed investments
Targets acquired without a cyber audit, portfolio companies without security oversight, value that can collapse at the first incident.
The Kumaiko approach
At Kumaiko, we don’t start with tools. We start with your business.
Our role: helping decision-makers understand the risks that really weigh on their business, and make informed decisions to manage them. An approach that is both strategic and operational, tailored to your context, built with your teams and actionable from day one.
- Critical activities
Identify the activities and processes that must keep running, even in a crisis.
- Cyber risks
Analyze the attack or failure scenarios likely to disrupt or degrade operations.
- Resilience
Measure the organization’s ability to absorb a major incident and recover.
- Prioritization
Direct budgets toward the actions that genuinely reduce risk.
- Execution
Support implementation and measure progress over time.
Your tools, your pace
No imposed tools: we work with the ones you already have, with standard office tools (spreadsheets, presentations) when they are enough, or with a solution chosen to fit your needs and budget. On every engagement, the tooling adapts to your maturity, not the other way around.
Our services
Concrete expertise
for your challenges.
From strategic framing to crisis management, we step in where you need us: for one-off engagements, long-term support or as a fractional CISO. Each engagement is scaled to your challenges, brings in the right expertise and translates into concrete, prioritized and trackable actions.
-
Cyber strategy & governance
- Security organization and roles
- Security policies and processes
- Risk analysis (EBIOS RM, ISO 27005, IEC 62443-3-2 for industrial environments)
- Maturity assessment and roadmap
- Fractional CISO (outsourced CISO)
-
Compliance
- Regulations: GDPR, NIS2, DORA, CRA, AI Act
- Certifications and frameworks: ISO 27001, SOC 2, TISAX, AirCyber, SWIFT CSP
- Audit and certification readiness
- End-to-end compliance support
-
Resilience & business continuity
- Business impact analysis (BIA)
- Business continuity plan (BCP)
- IT disaster recovery plan (DRP)
- Crisis tests and exercises
-
Cyber program management
- Security program management (PMO)
- Stakeholder coordination
- Roadmap tracking and executive reporting
-
Cyber crisis management
- Setting up the crisis management team
- Coordinating internal teams and service providers during cyber crises
- Reporting to executives and shareholders
- Post-incident lessons learned
-
Due diligence & portfolio security
- IT and cyber due diligence ahead of an acquisition, an investment or an exit
- Cyber maturity assessment of portfolio companies
- Portfolio cybersecurity program
- Remediation plans: design, implementation support within portfolio companies and reporting to investment committees

Who we work with
Kumaiko works with those who make decisions, and those who prepare them.
-
Executives
Grow the business without exposing the company to poorly controlled risks. Understand cyber issues in business terms, not technical ones.
-
Investors
Understand cyber risk before it becomes financial risk: before an acquisition or an investment, throughout the holding period, and up to the exit.
-
CIOs
Secure information systems while supporting business needs. Prioritize with real resources and budget constraints.
-
CISOs
Turn technical findings into concrete decisions. Convince leadership, structure the plan, drive execution, and get support when resources are stretched.
-
Legal & compliance
Understand IT and cyber jargon, move forward confidently with compliance and build the evidence expected during an audit.
References
They trust us.
Finance, industry, services, public sector, in France and internationally: a few words from those we have supported. For confidentiality reasons, some testimonials are anonymized.
-
Cyber coordination & program management
Throughout the whole planning process, you have been an incredible support. Your continued coordination, responsiveness and commitment have made a real difference. There have been a lot of moving parts, and your support throughout has been greatly valued by the entire team.
Director, Cyber Security & Risk ManagementInternational organization, preparation of a major event
The firm
Kumaiko
Kumaiko is an independent cybersecurity consulting firm, specializing in IT and OT (industrial systems) environments. It was founded by Camille Taste, who has been supporting organizations in France and internationally since 2015.
We act as fractional CISO and support executive teams, investors and security, IT, legal, compliance, data protection and risk teams on strategic and operational engagements. For projects that require it, we build a tailored team with expert consultants from our network.
Kumaiko is built on the idea that cyber consulting should be grounded in the field, results-driven and useful to the business. Strategic when you need to think ahead, operational when you need to act fast.
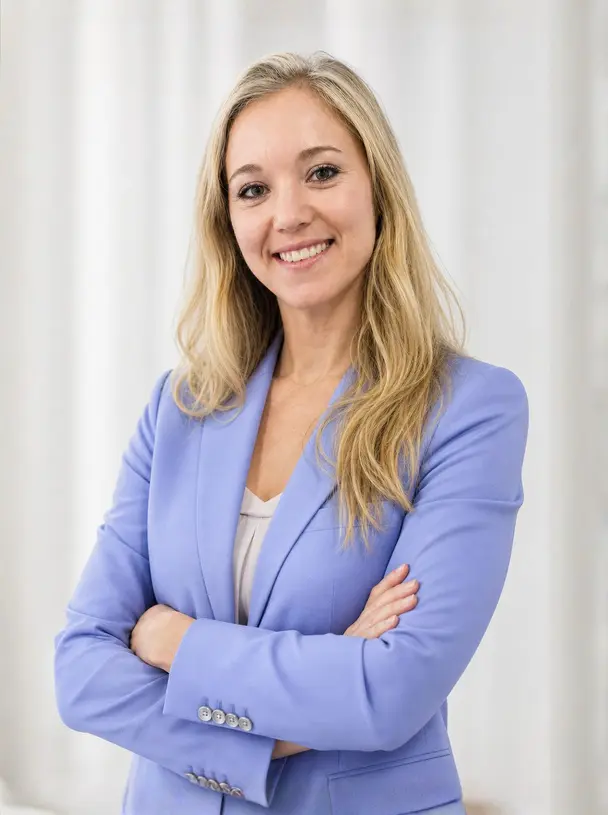
- 10 years of cybersecurity experience
- CISO experience, in-house and outsourced
- Big Four and consulting background, in France and internationally
- IT and OT expertise
- Network of 15+ expert consultants
- Cross-industry: finance, industry, services, public sector
FAQ
Your questions, answered.
What is a fractional CISO?
A Chief Information Security Officer who works with you a few days a month, according to your needs. It suits organizations that need expert cybersecurity leadership without hiring a full-time CISO.
Is my company subject to NIS2?
The European NIS2 directive extends cybersecurity obligations to many medium and large companies across 18 sectors. It also makes executives accountable. We help you determine whether you are in scope and what it means in practice.
What is the difference between ISO 27001 and SOC 2?
ISO 27001 is an international standard used to certify how your security is organized. SOC 2 is an audit report, widely requested by North American customers, that attests to the effectiveness of your controls. We help you choose the framework that fits your customers and markets, then achieve it.
What is cyber due diligence?
It is the assessment of a company’s security level and cyber risks ahead of an acquisition, an investment or an exit. It identifies the risks that could affect the value of the deal and prepares a remediation plan.
Do you work outside France?
Yes. We support organizations in France and internationally, in French and English.
Do we need specific tools?
We work with the tools you already have, making the most of your existing systems and standard office software wherever possible. When needed, we help you identify and implement solutions tailored to your specific needs, objectives, and budget.
Have a question about your cyber risks?
A 30-minute video call to take stock together.
No commitment, no jargon.
Or email us: contact@kumaiko.com